 agent-taskbay
Capability map
Every major Taskbay capability, its setup path, and the boundaries of current support.
Taskbay is a human operations console for remote A2A agents. It records commands before dispatch, follows durable tasks, and lets people supply input or decide approvals. It does not run or orchestrate your agents. This map links each major capability to the complete documentation.
Core operations
| Capability | Setup and behavior | Details and boundaries |
|---|---|---|
| Agent catalog and discovery | Register a card URL, inspect skills, interfaces, security schemes, compliance and trust. | Connect an agent. Extended-card capability is displayed but the extended card is not fetched. |
| Durable commands and tasks | Send, reply, cancel, revisit after closing the browser, retain history through restart. | Durable tasks. Dispatch, uncertain outcomes and duplicate handling are server-owned. |
| Streaming, reconciliation and freshness | Workers observe streams and poll open tasks, using a common idempotent ingestion path. | Workers. Non-streaming agents rely on polling. |
| Agent push callbacks | Configure callback origin and signing key; worker registers push for capable agents. | Push setup. Push authentication is separate from browser sessions and vault bindings. |
| Inbox, ownership and escalation | Claim and assign tasks, set due times and surface work needing attention. | Use the console, Human in the loop. Saved views, search and bulk triage are not implemented. |
| Human approvals | Review an exact immutable revision, approve/reject, expire or supersede outdated decisions, record rationale and delivery. | Human in the loop. A plain reply can bypass an open approval; approval does not prove agent-side execution. |
| Audit | Append-only facts about decisions, ownership and security actions. | Threat model. No built-in export, retention or tamper-evidence system. |
| Notifications | In-app notifications and one optional signed webhook channel for one organization. | Notifications. At-least-once delivery requires receiver deduplication and signature verification. |
| Artifact persistence and projection rebuild | Filesystem storage plus database records; reconstruct task projections from retained events. | Upgrading and backups, Workers. Back up the filesystem and database together. |
Following approval delivery
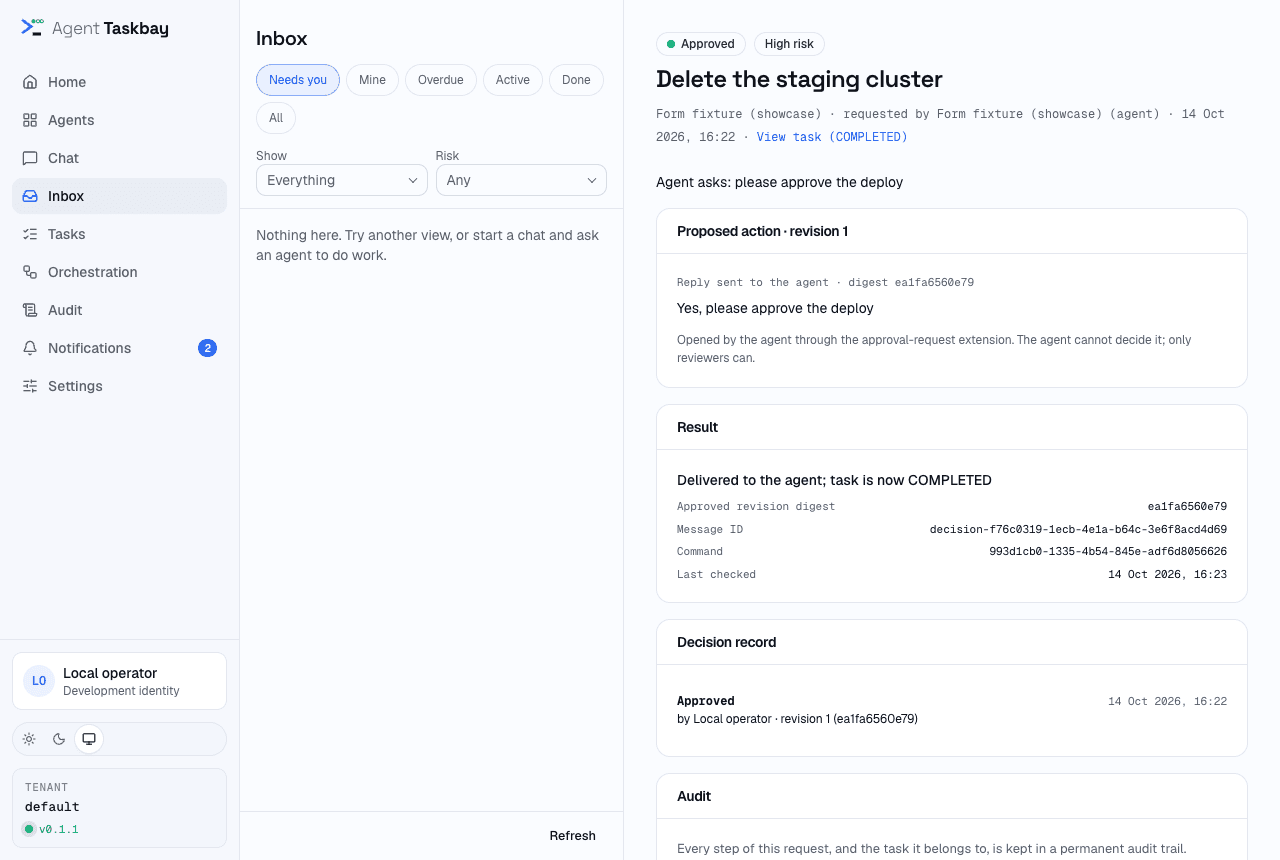
The console keeps the reviewed revision, decision record, delivery state and linked task together. This original fixture screenshot shows a delivered approval and the task's reported completion. Delivery confirms the reply reached the agent; it does not independently prove that the proposed action executed.
Identity and security
| Boundary | Supported | Limits |
|---|---|---|
| People → Taskbay | OIDC authorization code, S256 PKCE, RS256, client_secret_post; server-side sessions. | OIDC walkthrough. No SAML, passwords, SCIM, provider-claim role mapping or service API tokens. |
| Human authorization | Admin/operator/viewer, teams, organization/member/team grants, whole-agent and skill scopes. | Teams and grants. Skill isolation requires a cooperating agent; one organization per deployment. |
| Taskbay → agent | API-key header, bearer, OAuth client credentials or mTLS, encrypted and bound to exact origins. | Protected agents. One service binding per agent; no delegated OAuth or automatic AUTH_REQUIRED flow. |
| Card identity | Origin-pinned public JWKs with key ID, algorithm and expiry; optional signed-card requirement. | Agent credentials. RS256, ES256, EdDSA; no fetching keys from card URLs. |
| Outbound network | Exact origin allowlist, connection-time DNS checks, HTTPS, explicit private-network opt-in, size limits, redirect rejection. | Configuration. Reserved/metadata addresses remain blocked. |
| Deployment secrets | Separate flow/vault/push/notification keys and encrypted credential storage. | Environment map. Host configuration is trusted; built-in KMS integration is absent. |
Rich content and agent extensions
| Capability | Activation | Current support |
|---|---|---|
| Rich content | Core renderers and user-selected views. | Rich content: text, Markdown, JSON, CSV, images, media, PDF and files; opt-in sanitized inline HTML and isolated styled HTML preview. No agent script execution or remote-media proxy. |
| Structured input | Agent advertises structured-form extension. | Structured forms. Experimental; unknown or invalid content remains data. |
| Agent-originated approval | Agent advertises approval-request extension. | Approval requests. Experimental; not an AG-UI approval interrupt or framework-specific pause adapter. |
| Skill routing | Agent advertises and enforces the extension. | Skill routing. Taskbay selects a bounded skill; the agent must honor it. |
| A2UI | Agent provides the supported v0.9 subset. | A2UI reference. Experimental; chat surface only, incomplete component/function set, no real-agent verification. |
| Sideband and trace events | Built-in URNs plus optional extra negotiated URIs. | Extension reference. Additional extensions require code changes; there is no plugin contract. |
| AG-UI adapter | Set A2A_AGUI_ENABLED=true. | AG-UI reference. Experimental: same-origin authenticated clients, text input, basic interrupts/resume, 50-second runs; no skill-scoped principals, real-client verification or approval interrupts. Durable tasks can continue after the stream ends. |
Protocol and hosting
JSON-RPC and HTTP+JSON transports are supported through the official A2A SDK. Version 1.0 cards are exercised by fixtures; v0.3 is normalized through legacy compatibility but has not been verified against real v0.3 agents. gRPC is rejected under the hardened network policy.
Use npx agent-taskbay and single-owner PGlite for local operation. Use a source checkout, PostgreSQL, OIDC, a supervised web process, supervised workers and shared artifact storage for team deployments. The npm package does not include the operator scripts. Container images, Compose/Helm packaging, managed hosted service, object storage and measured horizontal-scale guarantees are not provided by this version.
Upstream CI covers Node.js 22.19 and PostgreSQL 18 on Linux. Cross-browser, macOS, Windows, particular OIDC providers and a broad range of third-party agents are not verified. The application is pre-1.0 and has not had an independent security review.
Source of truth
This map follows Compatibility, Status and roadmap, Threat model and the source at a52de4c. Those pages retain the detailed issue links, test evidence and planned work.
Created and maintained by Shashi Kanth G S at allsrc.dev. Visit shashikanth.me.
Connect an OAuth-protected agent
Register a protected Agent Card, configure a client-credentials binding, verify discovery, and manage rotation.
Overview: what Agent Taskbay is
For readers who want the mental model before they install anything: what the project does, what it leaves to other systems, and how the pieces fit together.